Call CA Tally HelpDesk
+91 9205471661,
7428779101
Introduction: Why Data Privacy Matters for Every Business
Every business depends on trust. Customers share names, addresses, telephone numbers, billing information and payment details because they expect organisations to handle that information responsibly.
At the same time, businesses maintain confidential accounting records, supplier information, employee details and financial statements.
If this information is accessed without authorisation, accidentally deleted or disclosed improperly, the consequences can be serious.
Small businesses are particularly vulnerable when accounting files are shared casually, passwords are reused or employees receive more access than their responsibilities require.
Data privacy and accounting security are essential foundations of responsible business management.
Privacy concerns how personal information is collected, used, shared and retained. Security concerns the safeguards that protect information from unauthorised access, alteration, loss or misuse.
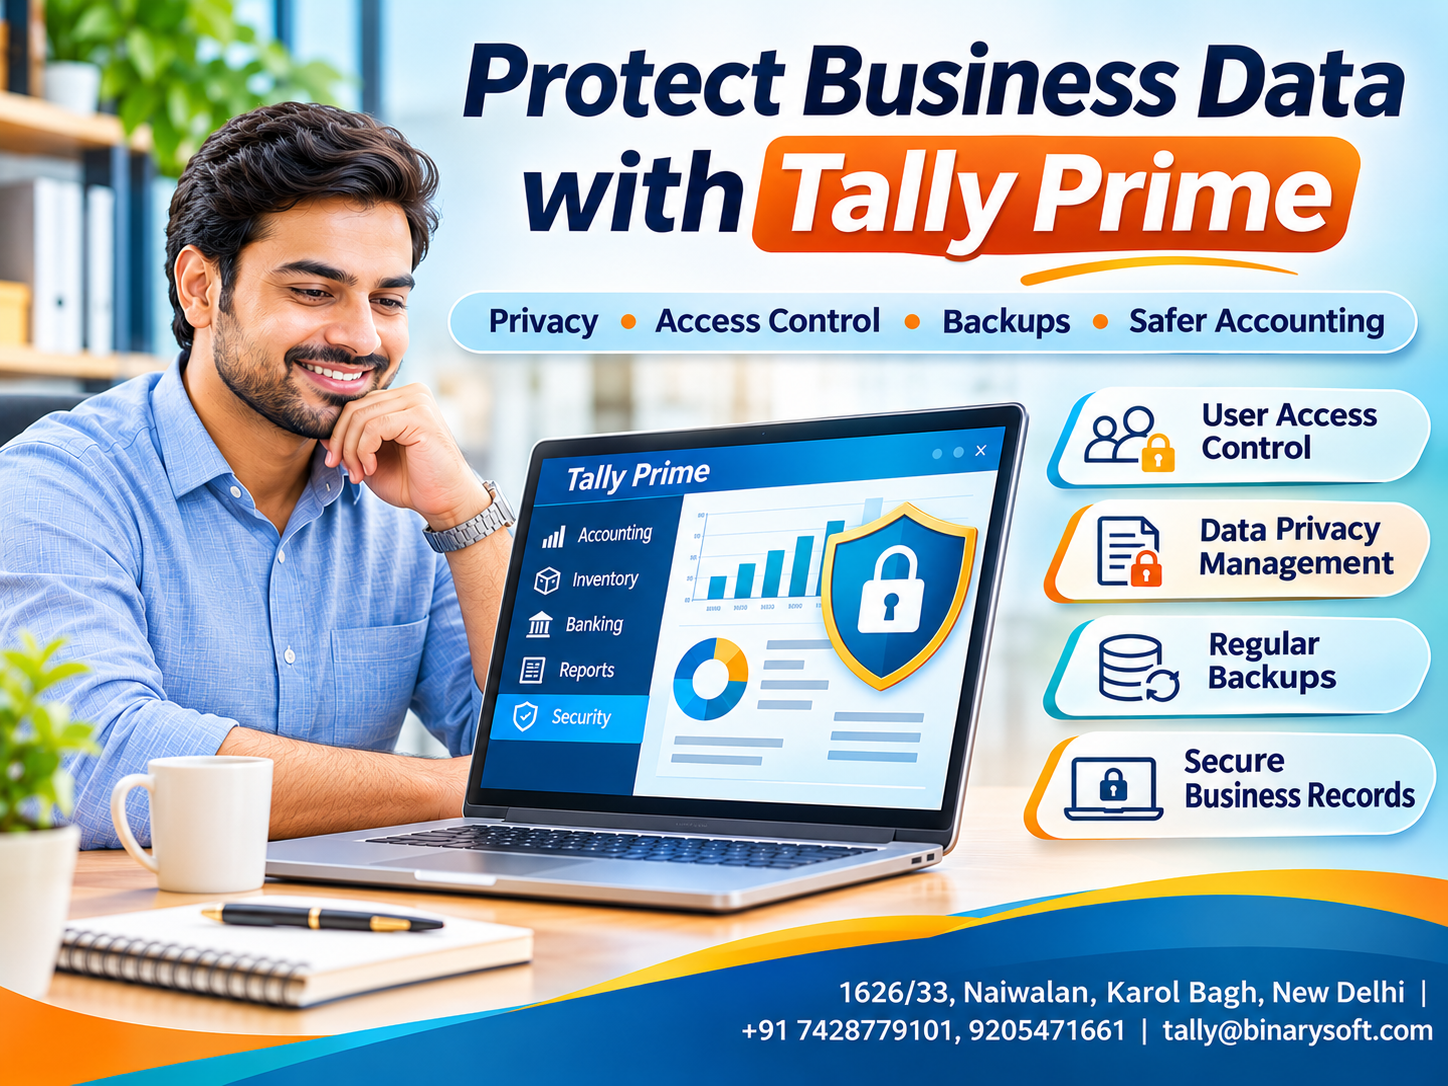
Tally Prime offers features that can help businesses manage access to accounting records and maintain backups.
However, software security alone is not enough.
Businesses must also establish clear privacy procedures, train employees, protect devices and comply with applicable legal requirements.
This guide explains practical approaches to protecting financial and personal information while using Tally Prime.
1. What Is Data Privacy in Business Accounting?
Data privacy refers to the responsible handling of information relating to identifiable individuals.
In business accounting, this may include customer names, contact information, addresses, bank-related details and transaction records.
Some accounting information concerns businesses rather than individuals, but it may still be commercially confidential.
An effective privacy approach begins by understanding what information is collected and why.
Important Privacy Principles
Purpose Limitation: Collect information for legitimate and clearly defined business purposes.
Data Minimisation: Avoid requesting unnecessary personal details.
Restricted Access: Allow employees to access information relevant to their responsibilities.
Transparency: Explain how personal information is used and shared.
Retention Control: Keep information only for appropriate periods, subject to legal obligations.
Accountability: Establish procedures for handling privacy requests and incidents.
These principles help organisations reduce unnecessary exposure of sensitive information.
2. Types of Information Businesses Should Protect
Businesses maintain several categories of important information.
|
Information category
|
Examples
|
|---|
|
Customer information
|
Names, contact details, billing addresses
|
|
Supplier information
|
Contact records, payment details
|
|
Financial records
|
Sales, purchases, payments, balances
|
|
Employee information
|
Payroll-related records and contact details
|
|
Tax information
|
GST-related records and statutory identifiers
|
|
Business information
|
Pricing, margins, inventory and reports
|
Not all information has the same sensitivity.
For example, employee payroll records may require stricter access controls than general stock summaries.
Businesses should identify sensitive records and establish appropriate protection measures.
3. How Tally Prime Supports Accounting Data Security
Tally Prime provides security-related capabilities that help organisations control access to company data.
These include company security settings, user management and role-based permissions.
Depending on the software release and configuration, businesses can also use additional features for monitoring or protecting accounting records.
Practical Benefits
A business owner can restrict access to selected functions.
An accounts employee may receive permissions needed for routine voucher entry.
A manager may require access to financial reports.
An administrator may be responsible for maintaining user accounts and security settings.
Separating responsibilities reduces unnecessary access and supports internal accountability.
Security controls must be configured correctly to provide the intended protection.
4. Configure User Access and Permissions
Giving every employee unrestricted access to accounting data creates avoidable risk.
Businesses should follow the principle of least privilege.
This means users receive only the permissions necessary to perform their duties.
Practical Configuration Steps
-
Open the relevant company in Tally Prime using an authorised administrator account.
-
Enable the applicable security controls.
-
Configure user roles and permitted activities.
-
Create individual user accounts where supported.
-
Assign permissions according to job responsibilities.
-
Test access using the relevant user roles.
-
Review permissions whenever responsibilities change.
For example, an invoice operator may need sales-entry access without permission to alter important administrative settings.
The exact configuration screens may differ by software release.
5. Protect Accounting Data with Strong Password Practices
Passwords remain an important security control.
Weak or shared passwords increase the risk of unauthorised access.
Businesses should use strong, unique passwords and avoid storing credentials in unprotected documents.
Employees should never share administrator passwords through informal messaging channels.
When an employee leaves the organisation, their access should be disabled promptly.
Where supported, additional authentication measures should be enabled for related accounts and connected services.
Password security should extend beyond accounting software to computers, email accounts and backup systems.
6. Maintain Regular and Reliable Data Backups
Accounting data may be lost because of hardware failure, accidental deletion, malware or operational mistakes.
Regular backups help businesses recover information after unexpected incidents.
Tally Prime supports company data backup and restoration procedures.
Recommended Backup Practices
Businesses should establish a schedule based on transaction volume.
A high-volume distributor may require daily backups, while a smaller organisation may adopt a different frequency.
Backups should be stored in secure locations separate from the primary system.
At least one protected copy should be maintained independently of the computer used for daily accounting.
Businesses should also test restoration procedures periodically.
A backup that cannot be restored may provide little practical protection.
7. Understand Privacy Risks in Digital Accounting
Digital accounting improves efficiency but introduces responsibilities involving devices, networks and data sharing.
Potential risks include phishing emails, malicious attachments, insecure remote access and unauthorised file transfers.
Employees may accidentally send customer statements to the wrong recipient or upload confidential records to an unapproved service.
Risk Reduction Measures
Use updated operating systems and security software.
Restrict installation of unapproved applications.
Avoid accessing confidential accounting information through unsecured devices.
Verify recipients before sharing financial documents.
Use secure transfer methods for sensitive files.
Maintain procedures for reporting suspicious activity.
These measures complement the security controls available within accounting software.
8. Responsible Collection of Customer Information
Businesses often require customer information for billing, delivery, support and statutory compliance.
However, collecting unnecessary details can increase privacy risks.
For example, a retailer preparing an invoice should request only information appropriate for the transaction and applicable legal requirements.
Customer information should not automatically be reused for unrelated marketing activities.
Businesses should explain relevant processing purposes and provide appropriate notices where required.
When information is shared with service providers, suitable safeguards and contractual arrangements may be necessary.
9. Data Retention and Secure Disposal
Business information should not be retained indefinitely without a valid reason.
However, accounting and tax records may be subject to statutory retention requirements.
Businesses must distinguish between information that can be deleted and records that must be preserved.
Practical Retention Approach
Identify the categories of information held.
Determine applicable legal and operational retention requirements.
Establish documented retention periods.
Restrict access to archived information.
Delete or securely dispose of records when retention is no longer justified.
Retention policies should also address backups, exported reports and paper documents.
Businesses should seek appropriate professional advice before deleting statutory records.
10. Privacy, GST Records and Financial Compliance
GST-related accounting records may contain customer and supplier information, invoice details and transaction values.
Businesses must protect these records while meeting applicable compliance obligations.
Tally Prime supports GST-related accounting and reporting, but the organisation remains responsible for correct information handling.
Tax documents should be shared only with authorised individuals or entities for appropriate purposes.
Businesses should also verify legal retention requirements before removing older records.
Privacy obligations and statutory recordkeeping duties must be considered together.
11. Emotional Story: A Business Owner Learns the Value of Customer Trust
Neha managed a small wholesale stationery business in Delhi.
Her father had built the company through decades of dependable service.
Customers trusted the family because orders were delivered on time and accounts were handled carefully.
As the business expanded, Neha introduced digital accounting.
However, employees continued sharing passwords and exchanging financial reports through informal channels.
One afternoon, a customer called to report that an account statement containing personal billing details had reached the wrong recipient.
Neha immediately investigated.
Although the incident involved a single document, she understood how easily customer confidence could be damaged.
That evening, she remembered her father's advice: trust takes years to build but can be weakened in a moment.
Neha decided to improve the company's information-handling procedures.
She reviewed employee permissions, introduced individual accounts where appropriate and established rules for sharing customer statements.
The company also strengthened backup procedures and trained employees to verify document recipients.
Over time, staff became more careful about handling customer information.
Neha could not guarantee that mistakes would never happen again, but she had created a more responsible system.
For her, protecting customer information became another way of honouring the trust her father had earned.
This fictional story illustrates the importance of privacy awareness and responsible accounting practices.
12. Case Study One: Improving Data Security in a Wholesale Business
Illustrative case study; not a verified customer outcome.
Business Background
A wholesale electrical goods distributor maintained accounting records for numerous customers and suppliers.
Several employees used the same computer and shared accounting credentials.
Challenges
Management could not easily distinguish employee responsibilities.
Financial reports were accessible to staff who did not require them.
Backups were performed irregularly.
Implementation
The business reviewed its Tally Prime security configuration.
Individual user permissions were introduced according to job responsibilities.
Administrative access was restricted, and a documented backup schedule was established.
Employees received basic training in password management and safe document sharing.
Illustrative Results
|
Area
|
Earlier practice
|
Improved practice
|
|---|
|
User access
|
Shared credentials
|
Role-based access
|
|
Financial reports
|
Broad availability
|
Restricted permissions
|
|
Backups
|
Irregular
|
Scheduled and reviewed
|
|
Document sharing
|
Informal process
|
Recipient verification
|
Key Learning: Appropriate access controls and consistent backup procedures help reduce avoidable accounting security risks.
13. Case Study Two: Protecting Client Records in an Accounting Firm
Hypothetical business scenario; no independently measured results.
Business Background
A small accounting consultancy managed financial records for multiple clients.
Employees frequently exchanged statements and accounting files while preparing reports.
Challenges
The firm needed stronger procedures for separating client information and managing access.
It also wanted more consistent backup and document-sharing practices.
Implementation
The organisation reviewed user permissions and established separate access procedures for relevant client records.
Employees were instructed to verify recipients before sending financial documents.
Backups were stored in protected locations, and restoration testing was introduced.
Illustrative Results
The firm developed clearer responsibilities for handling confidential information.
Staff gained a better understanding of privacy risks and appropriate sharing procedures.
Key Learning: Accounting confidentiality depends on software configuration, employee awareness and organisational policies working together.
14. Employee Training: An Essential Security Investment
Even well-configured software cannot prevent every human error.
Employees must understand why financial information requires careful handling.
Training should cover password security, phishing awareness, safe document sharing and suspicious activity reporting.
Staff should also learn how to recognise information that should not be disclosed without authorisation.
Suggested Training Topics
-
Protecting customer and supplier information
-
Recognising suspicious emails
-
Using individual accounting credentials
-
Sharing reports securely
-
Following backup procedures
-
Reporting lost devices or accidental disclosures
Training should be repeated periodically and updated when business processes change.
15. Privacy Considerations for Cloud and Remote Access
Remote accounting access can help business owners and employees work from different locations.
However, remote connectivity introduces additional security considerations.
Businesses should evaluate the security arrangements of any hosting or remote-access provider.
Important considerations include authentication, encryption, access permissions, backup responsibilities and incident response procedures.
Using Tally Prime through a remote or hosted environment does not automatically guarantee that all information is encrypted or protected against every threat.
The overall security of the arrangement depends on the complete technical environment and operational practices.
Businesses should understand where data is stored and who can access it.
16. Data Privacy Rights and Indian Businesses
India's Digital Personal Data Protection framework establishes obligations and rights concerning digital personal data, subject to the applicable provisions and their commencement.
Businesses should assess which requirements apply to their activities.
Relevant considerations may include providing appropriate privacy notices, handling consent where required and responding to applicable individual rights.
Organisations may also need procedures for complaints, corrections, erasure requests and personal data breaches.
Legal obligations can differ according to the organisation's role, processing activities and applicable regulations.
A generic online article cannot replace a properly drafted privacy notice or legal compliance assessment.
17. Create a Practical Data Protection Checklist
Businesses can improve privacy management through regular reviews.
|
Security area
|
Recommended action
|
|---|
|
User access
|
Review permissions and remove unnecessary access
|
|
Passwords
|
Require strong, individual credentials
|
|
Backups
|
Maintain and test secure copies
|
|
Software
|
Use supported releases and security updates
|
|
Customer information
|
Collect only necessary details
|
|
Document sharing
|
Verify recipients and use secure methods
|
|
Retention
|
Follow documented retention requirements
|
|
Training
|
Conduct periodic employee awareness sessions
|
|
Incident response
|
Establish reporting and escalation procedures
|
A checklist is most effective when responsibilities are assigned and completion is reviewed.
18. How Binarysoft Technologies Can Help
Binarysoft Technologies is an Authorized Tally Partner assisting businesses with Tally Prime-related requirements.
Organisations can discuss security configuration, user permissions, backup procedures and accounting workflows.
Areas of Assistance
Security Configuration: Understand available company security and access-control settings.
User Management: Configure appropriate permissions for accounting employees.
Backup Guidance: Establish suitable backup and restoration procedures.
Accounting Setup: Organise financial records and transaction workflows.
Employee Training: Improve understanding of relevant Tally Prime features.
Technical Assistance: Discuss software-related difficulties and configuration requirements.
Service scope, availability and applicable charges should be confirmed directly.
Conclusion
Data privacy and security are essential for maintaining customer confidence and protecting business information.
Accounting systems contain valuable financial records, customer details, supplier information and operational data.
Tally Prime provides security-related features that can help organisations manage access and protect accounting records.
However, responsible information management requires more than software alone.
Businesses must establish appropriate permissions, maintain reliable backups, train employees and follow applicable privacy and recordkeeping requirements.
Strong privacy practices reduce unnecessary risk and demonstrate respect for customers, employees and business partners.
With suitable configuration and disciplined procedures, businesses can use Tally Prime more confidently while strengthening their approach to accounting data protection.
Binarysoft Technologies can assist organisations in exploring practical security and accounting configuration requirements.
Powered by Binarysoft Technologies
Authorized Tally Partner
Location: 1626/33, 1st Floor, Naiwalan, Karol Bagh, New Delhi – 110005, INDIA
Contact Us: +91 7428779101, 9205471661
Email Us: tally@binarysoft.com
Business Hours: 10:00 AM – 6:00 PM, Monday to Friday
Frequently Asked Questions
What is data privacy in accounting?
Data privacy in accounting concerns the responsible collection, use, sharing, storage and retention of personal information contained in financial and business records.
Does Tally Prime provide security features?
Yes. Tally Prime supports company security settings, user management and access controls that can help protect accounting records.
Can businesses restrict employee access in Tally Prime?
Yes. Appropriate user roles and permissions can restrict access to selected accounting functions according to employee responsibilities.
Can Tally Prime be used securely through remote access?
It can be used in appropriately configured remote environments, but security depends on the hosting arrangement, authentication, network protection and other safeguards.
CA. Raghav Mundhra focuses on business accounting, GST reporting, and financial reconciliations. He works with organizations to strengthen accounting processes and maintain reliable financial information for compliance and decision-making.